Security · HSSE Watch
Cold-Chain Cybersecurity: Protect Physical Conditions, Not Just Data
Published
U.S. joint fact sheet dated 5 November 2026; Singapore CSA advisory published 6 November 2026. Reported attack period: October–November 2026; precise intrusion methods remain under investigation. Article/source review: 6 November 2026.
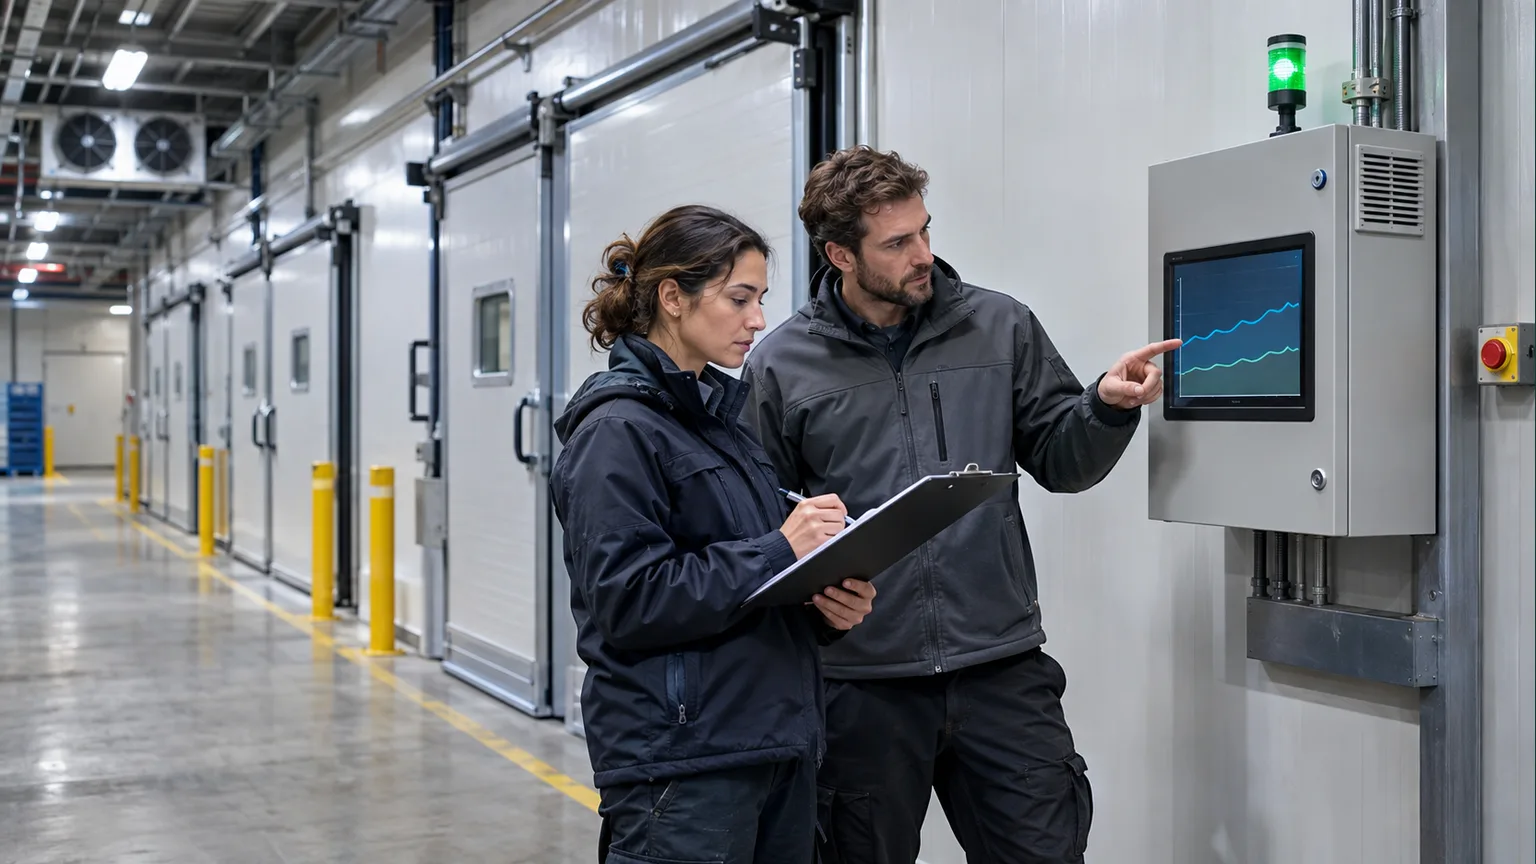
A refrigeration cyber incident is not only an IT problem. It can change a physical process while leaving operators unsure whether the displayed information is trustworthy. For teams responsible for food, medicines, chemicals or temperature-sensitive logistics, secure access and dependable operational response belong in the same conversation.
What changed on 5 and 6 November 2026
A joint U.S. government fact sheet dated 5 November warns of malicious activity against refrigeration and cold-chain monitoring globally. CISA, FBI, HHS, USDA and DOT describe potential changes to temperature and defrost operation, equipment hazards and loss of visibility into temperatures. These are possible attack effects, not a finding that every affected installation experienced them.
Singapore's Cyber Security Agency issued related guidance on 6 November. It discusses reported European incidents during October and November, while noting that precise intrusion methods across affected systems remain under investigation. Neither advisory establishes that a particular reader's installation is compromised, and this article does not attribute the attacks to a named actor.
Connect cyber ownership with operational consequences
The U.S. fact sheet recommends removing public internet exposure, segregating OT, strengthening credentials, patching, keeping tested offline backups, logging and reviewing safe setpoint ranges. Singapore also calls for restricted vendor access, monitoring configuration changes and rehearsed incident response. These are authoritative recommendations, not a newly enacted universal legal requirement.
Operations, engineering, IT/OT security, quality and the equipment provider should agree how those measures will be implemented safely. A refrigeration controller may support several rooms, products or customers. Treating it as an isolated office-computer issue can hide the physical consequences of changing or losing it.
A practical joint review
- Choose one real system. Trace the service from the refrigerated space to its controller, network connection, remote support arrangement and alarm recipients. Reconcile the records with what competent personnel find, without attempting unauthorised scanning or access.
- Give remote access an accountable owner. Confirm the business need, authorised users, scope and review date. Ask who can end a supplier's access when a contract or task finishes. Refer technical changes to the responsible OT specialists.
- Define the safe response before disruption. Identify the approved action if temperatures depart from limits, readings become unavailable or displayed values conflict with trustworthy evidence. Do not invent a fallback operating mode during an incident.
- Separate equipment recovery from product release. Restored cooling does not itself prove that stored material remained acceptable. The authorised quality or clinical function should assess exposure history and product-specific requirements before deciding disposition.
- Protect evidence and communications. Use the response plan to preserve relevant timestamps, logs and configuration records. Avoid improvised resets that could erase evidence or unexpectedly change the physical process.
Change controls must protect the plant too
Do not disconnect equipment, install firmware, revise setpoints or select manual control just because an advisory recommends stronger security. Have the responsible specialists assess dependencies, arrange an approved change window, establish rollback and check the resulting operation. Urgency requires coordination; it does not make an untested intervention safe.
A useful exercise is a two-part scenario: first an unexpected temperature alarm, then an unavailable or inconsistent display. Ask each function what evidence it needs, who it contacts and who has authority to restrict operations or hold stock. The objective is to expose gaps in decisions before a real disruption—not to simulate a cyberattack on live equipment.
Questions for your next readiness review
- Who knows every legitimate route for changing the controller?
- Would a loss of temperature visibility reach an accountable person promptly?
- Can quality decisions use reliable time-and-temperature evidence?
- Who authorises recovery, and who independently accepts the operational result?
Authoritative video
The FBI publishes The FBI and Partners Urge Hardening Industrial Refrigeration and Cold Chain Monitoring Systems. Its official page supplies the video and transcript. The privacy-enhanced player below is the same embed linked by the FBI; playback remains subject to YouTube availability.
FBI video and accessible transcript · Direct video link
Key takeaway
Secure the route into the controller, verify the physical condition and keep product-safety decisions separate from the IT recovery milestone.
Sources and dates
- CISA, FBI, HHS, USDA and DOT — joint refrigeration and cold-chain fact sheet (PDF) ↗As of 5 November 2026. Potential physical effects and recommended mitigations.
- Cyber Security Agency of Singapore — remotely accessible OT control systems ↗6 November 2026. Reported incidents, uncertainty and cross-sector recommendations.
- FBI — official video and transcript ↗Publisher, exact title, direct YouTube URL and privacy-enhanced embed verified from the official FBI page.
- FDA — cybersecurity resiliency and cold-chain continuity ↗Supporting official context on FDA-regulated food and medical products, not a product-disposition instruction.
Sources checked 6 November 2026. Source statements and original practical applications are distinguished above. Always consult current official advice and applicable local requirements.
Share the lesson
Open the separate 9:16 Pinterest poster
Illustrative planning scene, not an actual incident or a technical procedure. HSSE TIPS branding appears only in the designed poster footer.
Your experience matters
Share your thoughts on this page
Have a question, a useful experience or a suggestion? Add your input below.
Comments are public. Keep them respectful and relevant. Do not share contact details, confidential information or emergency reports.
Comments on this page
Loading comments…